
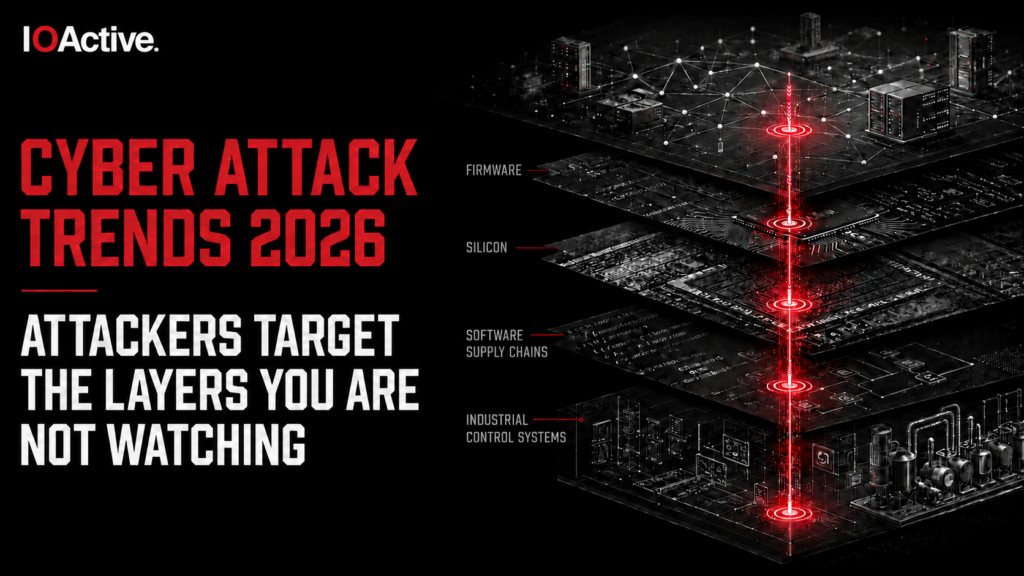
“The most significant cyber attacks of 2026 will target the systems organizations depend on most, not the systems they monitor most closely.”
Most cybersecurity forecasts treat ransomware, AI-enabled attacks, and supply chain risks as parallel threats of equal weight; a framing that produces the wrong priorities for security teams protecting complex organizations. The cyber attack trends in 2026 share a specific characteristic: they exploit environments organizations depend on most but monitor least, from industrial control systems running legacy protocols to firmware supply chains lacking integrity verification. This article evaluates which attack patterns represent confirmed, active risk across key threat categories.
| Threat | Key Risk Indicator | Level of Concern | Recommended Assessment |
| Ransomware Targeting OT and critical infrastructure | $74B global damage projected¹ | Escalating | Red team, OT security assessments |
| Software Supply Chain Attacks Build pipelines, open-source dependencies | $80.6B cost projection by 2026² | Underestimated | Secure development lifecycle (SDL) |
| OT/ICS Threats PLCs, RTUs, engineering workstations | 3,300+ industrial orgs impacted³ | Underdetected | OT/ICS security assessment |
| AI-Enabled Attacks Dev pipelines, social engineering | 31.6% of AI code fully exploitable⁴ | Mixed: some confirmed, some speculative | Secure code review, SDL |
| Critical Infrastructure Cyberattacks Energy, water, transport, defense | $4.82M average breach cost⁵ | Underreported | Full-stack ICS/OT assessment |
Ransomware: From File Encryption to Operational Disruption
Ransomware groups have moved beyond encrypting files and demanding payment. The operational model has shifted toward the targeted disruption of systems that organizations cannot quickly stop or replace.
Ransomware incidents reached 6,500 in 2025, up from under 1,400 in 2020, a more than 360% increase over five years.⁶ Global damage costs are projected to reach $74 billion in 2026, a 30% increase from $57 billion in 2025.¹ For organizations in critical sectors, the average breach cost stands at $4.82 million per incident, excluding production loss and regulatory response.
| Ransomware Characteristic | Traditional Model (Pre-2022) | 2026 Model | Recommended Assessment |
| Primary objective | File encryption, ransom demand | Operational disruption plus ransom | OT incident response planning |
| Target selection | Opportunistic, volume-based | Sector-targeted, timing-aware | Threat modeling |
| OT environment knowledge | Low | Active, documented reconnaissance | OT security assessment |
| Recovery timeline | Hours to days (IT) | Days to weeks (OT) | OT business continuity review |
| Payment pressure lever | Threat of data exposure | Extended process downtime | Red team exercise |
How Threat Groups Are Targeting OT Environments
The threat model has changed in a specific way. Groups with OT knowledge now time attacks around operational windows: peak demand periods for energy utilities, scheduled maintenance cycles at manufacturers, pre-harvest windows in agricultural processing. Dragos tracked 3,300 industrial organizations affected by ransomware in 2025.³ These are not random hits. They reflect adversaries who understand operational context well enough to maximize financial leverage.
What Separates Fast Recovery From Extended Downtime
Organizations recovering fastest from ransomware incidents are those that have run realistic OT continuity exercises against adversary scenarios. Applying untested IT recovery playbooks to industrial environments results in extended downtime because the two environments fail differently and recover on different timelines.
Software Supply Chain Attacks: The Dominant Third-Party Risk Vector
The SolarWinds compromise in 2020 demonstrated that trusted software update mechanisms could deliver malware to thousands of organizations simultaneously. The XZ Utils backdoor in 2024 showed that state-sponsored actors were willing to invest years in maintaining access to open-source projects before activating a payload. Neither incident was an outlier. Both represent a confirmed shift in how sophisticated threat actors approach access at scale.
| Supply Chain Attack Type | Notable Case | Detection Difficulty | Downstream Scope | Recommended Assessment |
| Software build tool compromise | SolarWinds (2020) | High | 18,000+ organizations | Secure development lifecycle (SDL) review |
| Open-source package backdoor | XZ Utils (2024) | High | Millions of Linux systems | Software composition analysis |
| Firmware implant | Vendor hardware (multiple) | Very high | Full device lifecycle | Firmware security assessment |
| AI model poisoning | Emerging (2025–2026) | Very high | Development pipelines | AI supply chain review |
| Hardware and silicon-level attack | AMD Sinkclose (2024)⁷ | Extremely high | Endpoint device fleets | Silicon security assessment |
Third-Party Risk Is Growing Faster Than Programs Can Track
Third-party involvement in security breaches rose from 15% to 30% in 2025.² Supply chain attack costs are projected to exceed $80.6 billion by 2026.² The attack surface is not shrinking: organizations now average over 1,000 third-party vendors, and the majority lack visibility into the security posture of their software dependencies beyond first-tier vendors.
One Compromise Can Expose Every Downstream Organization
The risk is systemic, not incidental. A single compromise of a widely used build tool, package manager, or firmware update process exposes every downstream organization that relies on it. Your environment’s security now depends in part on the security of every component that touches your build pipeline, whether or not you have audited it.
OT/ICS Threats: Adversaries Mapping Physical Processes
The 2026 Dragos OT Cybersecurity Year in Review documents a specific evolution in how adversaries approach industrial environments. They are no longer staging for future disruption. They are actively mapping control loops to understand how to manipulate physical processes with precision.³
| OT Threat Group | Primary Target Sector | Documented 2025 Activity | ICS Kill Chain Stage | Recommended Assessment |
| VOLTZITE | Electric, oil and gas | Gateway compromise, configuration extraction | Stage 2 | OT network security assessment |
| KAMACITE | Energy, water, heating (EU, US) | Four-month ICS reconnaissance campaign | Stage 1 | ICS threat hunting |
| ELECTRUM | Ukrainian, Polish infrastructure | Destructive wiper deployment (PathWiper)³ | Stage 2 | OT incident response planning |
| SYLVANITE | US utilities, SAP environments | Zero-day exploitation (CVE-2025-31324) | Stage 1 | Vulnerability assessment |
| BAUXITE | Israeli critical infrastructure | Dual wiper variants deployed | Stage 2 | Full-stack ICS/OT assessment |
Active OT Threat Groups
Three new OT threat groups emerged in 2025. Established groups expanded operations globally. Dragos now tracks 26 OT threat groups.³ KAMACITE conducted four months of sustained reconnaissance against US internet-exposed ICS assets, targeting specific device types in sequence. VOLTZITE compromised Sierra Wireless Airlink gateways across electric and oil-and-gas sectors, then pivoted to engineering workstations to extract configuration and alarm data. ELECTRUM deployed coordinated destructive wiper malware against eight Ukrainian ISPs and, in December 2025, Polish CHP facilities.³
Why Most Organizations Cannot See the Threat
The visibility problem is structural. Only 30% of OT networks have the monitoring capability to detect these threats before operational impact. 56% of organizations cannot see below the IT/OT boundary. 88% struggle with detection and response in OT environments.³
The Integrity Blind Spot Adversaries Exploit
IOActive’s research into OT security architecture has identified a persistent strategic blind spot. The standard AIC reordering (Availability-Integrity-Confidentiality) used in many OT environments prioritizes availability, which is precisely where the most capable adversaries operate. Stuxnet manipulated centrifuge speeds while feeding false readings to operators for months. Triton/TRISIS targeted Safety Instrumented Systems to remove the safeguard layer before causing process failure. Industroyer sent commands directly to substation equipment using native industrial protocols. All three targeted integrity, not availability, because integrity failures often go undetected, whereas availability failures trigger an immediate response.⁸
AI-Enabled Attacks: Separating Confirmed Risk From Speculation
AI’s role in offensive security requires more precision than most threat briefings provide. The meaningful 2026 risk is not the speculative scenario of fully autonomous AI attackers. It is the measurable deterioration in code security caused by AI-assisted development tools, and the accelerated pace at which phishing and social engineering campaigns now operate.
| AI Attack Vector | Operational Maturity | Documented Risk Indicator | Defender Priority | Recommended Assessment |
| AI-generated insecure code in production | High | 31.6% of samples fully exploitable⁴ | Critical | Secure code review, SDL |
| AI-accelerated phishing and spear-phishing | High | Volume and personalization increase confirmed | High | Social engineering assessment |
| Deepfake-based social engineering and fraud | Medium-High | Active in financial and executive targeting | High | Red team exercise |
| AI-assisted vulnerability discovery by threat actors | Medium | Being used by advanced groups | Medium | Threat modeling |
| Autonomous AI attack agents | Low | Demonstration cases only; no confirmed deployment at scale | Monitor only | No immediate action required |
AI-Generated Code Is Already a Security Liability
IOActive’s April 2026 whitepaper evaluated 27 leading AI models and AI-powered coding tools using 730 real-world programming prompts across 27 languages and 219 vulnerability categories. Security outcomes were measured against 72 automated vulnerability detectors, producing nearly 20,000 analyzed code samples. The results were direct: average security performance across all models was 59%, and 31.6% of AI-generated code samples were fully exploitable.⁴
No model achieved 100% secure output. Infrastructure and DevOps code (Dockerfiles, Terraform, CI/CD pipelines) produced the worst results, with vulnerability rates between 70% and 97%. Authentication, rate limiting, and cryptography consistently failed across nearly all models.⁴ According to IOActive’s research, GitHub Copilot is now generating nearly half of developers’ code.⁴ Organizations deploying AI coding tools without mandatory security review before production deployment are introducing exploitable risk at scale as a present, documented condition.
Where AI Is Accelerating Offensive Capabilities
The WEF Global Cybersecurity Outlook 2026 found that 87% of respondents identified AI-related vulnerabilities as the fastest-growing cyber risk over 2025.⁹ AI is accelerating phishing volume, enabling more convincing social engineering, and lowering the technical barrier for credential-based attacks.
Critical Infrastructure: The Widening Gap Between Visibility and Exposure
64% of organizations now account for geopolitically motivated cyberattacks against critical infrastructure in their 2026 risk strategies.⁹ 91% of the world’s largest organizations have changed their cybersecurity strategies due to geopolitical volatility.⁹ Awareness has grown. Technical detection coverage has not kept pace with it.
| Critical Infrastructure Sector | Primary 2026 Threat Vector | Current Avg. Visibility | Recommended Assessment |
| Energy (grid and generation) | OT compromise, wiper malware | Low (30% avg. OT visibility³) | Full-stack ICS/OT assessment |
| Water and wastewater | ICS manipulation, ransomware | Very low | OT network segmentation review |
| Telecommunications | Supply chain implants, espionage | Medium | Hardware and firmware audit |
| Transportation | Embedded system attacks, GPS manipulation | Low | Embedded systems assessment |
| Defense industrial base | Hardware supply chain, insider access | Variable | Silicon-level security review |
Active Campaigns Against Energy Infrastructure
The December 2025 coordinated attack on Polish CHP facilities and renewable energy management systems, attributed by Dragos to Russian state-linked actors consistent with ELECTRUM, confirmed that energy infrastructure in NATO-aligned countries is an active target.³ The same month, a new destructive wiper variant from ELECTRUM confirmed an active malware development pipeline. These are not isolated incidents: they reflect sustained, organized campaigns with documented capability to disrupt physical processes.
Where Conventional Monitoring Falls Short
IOActive’s critical infrastructure research spans SATCOM terminal vulnerabilities across aviation, maritime, and military systems; avionics security in DAL-A certified systems; and industrial control assessments across energy, chemical, and defense sectors. That body of work consistently surfaces the same pattern: the most consequential vulnerabilities reside in layers below where most monitoring tools operate. Software-layer monitoring does not detect the reconnaissance and lateral movement techniques being used by the most capable OT threat groups.
For organizations in these sectors, sophisticated adversaries have both the motive and the documented capability to access environments through the layers that receive the least security scrutiny. The more urgent question is whether that access is already established.
Frequently Asked Questions About Cyber Attack Trends 2026
Which of these five threat categories should security teams prioritize first?
OT/ICS threats and software supply chain attacks warrant the highest priority for organizations that have not assessed them recently, because both operate below the visibility threshold of most existing monitoring tools. Ransomware remains the highest-volume threat. AI-enabled attacks require immediate attention in development pipelines. Specifically, autonomous-AI attack scenarios do not warrant the same urgency as the confirmed, active attack patterns documented above.
How should security teams distinguish real business risk from vendor-amplified hype?
Apply two tests. First: Does the threat have documented, confirmed use in real environments, not proof-of-concept demonstrations? Second: Does it target environments your organization depends on but under-monitors? Threats that pass both tests warrant defense investment. Threats that fail the first should be tracked, but should not displace attention from attack patterns already operating at scale.
What makes IOActive’s perspective on attack trends distinct from standard threat intelligence reports?
IOActive’s assessments are grounded in research spanning hardware, firmware, embedded systems, industrial control systems, and live adversarial engagements across industries. Most threat intelligence derives from network-layer telemetry. IOActive’s research includes silicon-level attack techniques, OT protocol analysis, and hardware supply chain evaluation, which is where the most consequential vulnerabilities in 2026 are concentrated. Learn more about IOActive’s Full-Stack Security Assessment approach.
Attackers Target the Layers You Are Not Watching
The cyberattack trends in 2026 share one thing in common: they target the layers that most organizations aren’t watching. IOActive’s research spans silicon, firmware, OT, and live adversarial engagements, giving security teams a complete picture of where real exposure exists and what to do about it.
Sources
1. Cybersecurity Ventures, via SLCyber (2026). The True Cost of a Ransomware Attack in 2026. https://slcyber.io/blog/the-true-cost-of-a-ransomware-attack-in-2026/
2. Vectra AI / Think Ahead Tech (2025–2026). Supply chain attack cost and third-party breach data. https://www.vectra.ai/topics/supply-chain-attack; https://think-ahead.tech/en/blog/software-supplychain-security
3. Dragos. 2026 OT Cybersecurity Year in Review. https://www.dragos.com/ot-cybersecurity-year-in-review
4. IOActive. The Security Gap in AI-Generated Code (April 2026). https://www.ioactive.com/the-security-gap-in-ai-generated-code/
5. IBM. Cost of a Data Breach Report 2025, via StationX. https://app.stationx.net/articles/ransomware-statistics
6. Industrial Cyber. Hacktivists and Cybercriminals Expand Attacks on ICS, OT, and AI Systems Across Critical Infrastructure. https://industrialcyber.co/reports/hacktivists-and-cybercriminals-expand-attacks-on-ics-ot-and-ai-systems-across-critical-infrastructure/
7. IOActive. Tales from the Call Gate: AMD Sinkclose Vulnerability (2024). https://ioactive.com/tales-from-the-call-gate-an-smm-supervisor-vulnerability/
8. IOActive. Rethinking the CIA Triad in Operational Technology Environments (2026). https://www.ioactive.com/rethinking-the-cia-triad-in-operational-technology-environments/
9. World Economic Forum. Global Cybersecurity Outlook 2026 (January 2026). https://reports.weforum.org/docs/WEF_Global_Cybersecurity_Outlook_2026.pdf